Certification for healthcare and life sciences
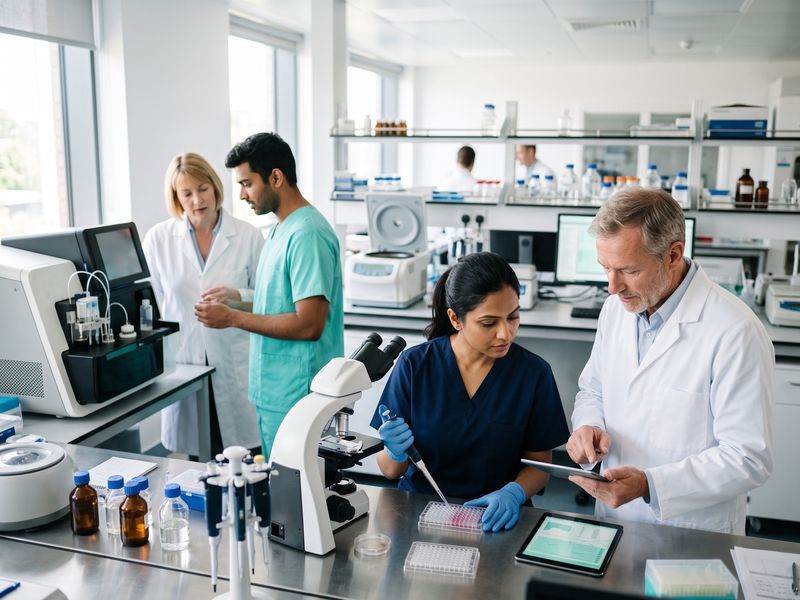
Healthcare, medical devices and life sciences operate under intense scrutiny, and certification is part of how organisations prove they meet it. For medical device manufacturers, a recognised quality management certificate is frequently a prerequisite for market access and for the relationships that sit upstream and downstream of you. For digital health and clinical-data businesses, information security certification reassures partners and regulators that sensitive data is protected.
Which standards are relevant
Medical device organisations typically pursue ISO 13485, the sector-specific quality management standard for design and manufacture of medical devices. Where an organisation handles sensitive health data — increasingly the case for digital health platforms — ISO 27001 for information security applies alongside it. Some organisations also hold ISO 9001 for broader quality management across non-device activities.
What makes a healthcare audit different
Audits in this sector carry a heavier emphasis on traceability, risk management and documented control, reflecting the regulated nature of the work. For ISO 13485, auditors look closely at design controls, supplier management, and the handling of complaints and corrective actions. For information security in clinical settings, the focus falls on protecting patient and research data across systems and partners. Because patient safety and data protection are the stakes, the evidence bar is exacting — which is also why a clean, independently audited certificate carries weight with buyers.
How ABS helps
We prepare medical device and health-data organisations for certification: a gap assessment against ISO 13485 and ISO 27001, design, risk-management, supplier and complaint-handling controls with the traceability auditors expect, data-protection controls across systems and partners, internal audits and a readiness check, then support through the certification body’s audits.
Common questions
How is ISO 13485 different from ISO 9001?
ISO 13485 is built specifically for medical devices, with stronger requirements around risk management, design controls and regulatory documentation. Organisations sometimes hold both — ISO 9001 for general quality and ISO 13485 for device-specific activities.
Do digital health platforms need ISO 27001?
If you store or process health data, ISO 27001 is the recognised way to demonstrate that information security is managed to an auditable standard — and partners increasingly require it.
Are on-site visits required?
Quality audits for device manufacturing usually include a site visit to observe controls in operation, while information security elements can often be assessed remotely. We confirm the approach with you upfront.